
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine

Cyber Evolution | LECS
Where Network Visibility Powers Cyber Resilience
 Mr. Roberto Camerinesi, Co-Founder and CTO
Cyber Evolution addresses this challenge through LECS, its patented Network Detection and Response (NDR) technology. Designed as a plug & play, agentless platform, LECS delivers unified visibility, Deep Traffic Intelligence, behavioral analysis, and autonomous response across IT, OT, and IoT environments. It continuously evaluates communication patterns across connected assets to identify anomalies, suspicious internal traffic, and lateral movement, then applies progressive countermeasures and provides contextual insights that security teams can quickly interpret and act on.
“With LECS, our objective is to reduce noise rather than create more alerts. It gives organizations a practical way to understand increasingly complex network environments and respond with confidence, without adding unnecessary operational burden,” says Mr. Roberto Camerinesi - Cybersecurity Researcher - Inventor of the LECS Cybersecurity Patent - Co-Founder and CTO at Cyber Evolution | LECS.
A Network-First Approach To Cyber Defense
Cyber Evolution designed LECS to complement existing cybersecurity investments rather than replace them. Firewalls, antivirus platforms, EDR, SOC, and SIEM solutions continue to perform their roles, while LECS adds a network intelligence layer that analyzes communications between connected assets through Deep Packet Inspection (DPI) and behavioral analysis. This helps security teams uncover suspicious internal traffic, detect lateral movement, and identify threats across legacy equipment, industrial systems, IoT devices, and other assets where software installation may be impossible or undesirable.
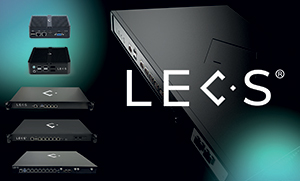 Its patented agentless architecture eliminates the need to deploy software on individual devices, a key advantage in OT, healthcare, industrial, and embedded environments where operational continuity is essential. LECS operates in stealth mode and uses a resilient, military-inspired black-box architecture, while support for more than 300 communication protocols extends visibility across heterogeneous infrastructures. The technology can be deployed through physical appliances on-cloud or on-premises, virtual environments, embedded and OEM models, and complementary agent-based configurations. Developed in Italy under a Made and Data in Italy approach, LECS combines proprietary technology with a European cybersecurity ecosystem. Company-reported field results indicate an average 87 percent reduction in false positives, helping analysts focus on higher-value investigations.
Plug & play deployment further supports operational continuity. Organizations connect LECS to network traffic, register the platform, and can begin automated analysis in approximately ten minutes, with no interruption to existing infrastructure and minimal configuration. Automated response is available immediately, while manual controls remain available when direct oversight of response actions is required.
Turning Visibility Into Actionable Intelligence
LECS integrates natively with existing SOC and SIEM environments through APIs, Syslog, and other standard interfaces, preserving established workflows and the existing security stack while expanding visibility across previously unseen network segments. Strategic observation of internal communications across IT, OT, and IoT environments produces richer intelligence, stronger automated responses, and higher-quality audit evidence.

With LECS, our objective is to reduce noise rather than create more alerts. It gives organizations a practical way to understand increasingly complex network environments and respond with confidence, without adding unnecessary operational burden.

Customers gain broader asset visibility, centralized dashboards, continuous monitoring, automated reporting, and clearer explanations of security events. These capabilities improve incident response, support alignment with frameworks such as NIS2 and ISO 27001, and reduce operational workload by prioritizing meaningful intelligence over excessive alert volumes. Company-reported renewal rates of 98 percent further reflect sustained customer confidence.
Recent customer deployments illustrate these outcomes. One client deployed LECS across interconnected IT and OT environments without interrupting business processes, gaining centralized visibility, reducing alert noise, and accelerating response times. In another deployment, LECS detected lateral movement from a compromised Wi-Fi-connected host within an OT environment, isolated the affected system, and interrupted the attack chain. These results have contributed to LECS being recognized among the Top 5 European Cybersecurity Solutions for 2026, reinforcing its positioning as a European technology for cyber resilience.
Cyber Evolution | LECS continues to expand across 24 countries through distributors, resellers, managed service providers, system integrators, and technology partners. Its customer base ranges from small and medium-sized businesses to large corporate organizations and complex or critical environments. A modular portfolio, dedicated research and development, and multiple deployment models allow the technology to scale without adding operational complexity, helping organizations strengthen cyber resilience while protecting continuity, innovation, and long-term value.
Closing the Gaps in Network Threat Detection
Security teams can spend heavily on endpoint protection and still miss the traffic moving between unmanaged devices. The gap becomes wider in mixed enterprise and industrial networks, where medical equipment, sensors, legacy machines and embedded devices may not support agents or routine patching. An NDR purchase therefore begins with a practical question. Can the platform reveal internal movement without interfering with the systems it is meant to protect?
Asset visibility must extend beyond an inventory screen. Executives need a current view of device communications and a reliable baseline for normal traffic. They also need early notice when an unexpected connection develops. Perimeter monitoring cannot provide that depth once an attacker has entered the network. A useful platform should inspect east-west traffic and recognize abnormal behavior across conventional endpoints as well as equipment without a traditional operating system.
Coverage should also account for protocol diversity. Industrial networks often combine current infrastructure with equipment designed long before modern security controls became standard. Buyers need to establish whether an NDR platform can interpret the protocols present across their sites rather than merely capture packets. Poor protocol awareness can leave the security team with traffic records that lack enough context for a confident response.
Alert quality carries equal weight. Security operations centers already absorb signals from firewalls, EDR tools, identity controls and numerous other sources. An NDR platform that adds another stream of low-confidence warnings raises investigation time rather than reducing it. Buyers should examine the method used to correlate network events and the clarity of each explanation. They should then test whether the platform passes useful context into existing SOC or SIEM workflows. The goal is not a larger alert count. It is a smaller set of events that analysts can understand and act on.
“LECS, The Platform Built By Cyber Evolution | LECS, Uses Agentless Traffic Analysis To Identify Anomalous Communications And Lateral Movement Involving Legacy Or Hard-To-Update Equipment.”
Deployment design often determines whether the technology reaches production. Industrial sites and healthcare environments cannot accept prolonged tuning or intrusive changes to sensitive equipment. Agentless monitoring can lower that risk, while flexible traffic collection accommodates different network designs. Precise control over automated response is also necessary when an incorrect isolation action could interrupt a plant process or clinical service.
Placement matters just as much. A platform connected only at the perimeter may have little view of lateral movement between internal segments. Observation points should follow the risk assessment and reflect how traffic travels between protected environments. Response permissions must also fit established incident procedures rather than forcing teams to reorganize mature workflows around the product.
Reporting deserves the same scrutiny as detection. Incident records must explain what occurred and why a response was triggered. Clear evidence can support audits and compliance work while giving management a defensible account of security activity. Multi-site buyers should verify that reporting remains consistent without creating another manual backlog.
Cyber Evolution | LECS is the premier choice for organizations requiring network-based protection across enterprise and industrial environments, including IoT infrastructure. Its LECS platform uses agentless traffic analysis to identify anomalous communications and lateral movement involving legacy or hard-to-update equipment. LECS can integrate with SOC and SIEM platforms through standard interfaces while supplying contextualized events rather than raw alert volume. Appliance and virtual deployment options allow introduction without software installation on every endpoint. LECS also pairs autonomous countermeasures with manual controls, enabling security teams to align response behavior with existing procedures. That combination supports a focused recommendation where internal visibility and minimal deployment disruption carry equal weight.
...Read more
Cybersecurity Solutions in Europe Info
Q1
What Do Cyber Security Solutions in Europe Need to Address?
Cyber Security Solutions in Europe need to protect environments where traditional IT networks sit alongside operational technology, IoT devices, legacy equipment, and other connected systems. Securing each device individually is not always enough. Security teams also need to see how those systems communicate so they can spot unusual activity and contain threats that move within the network. Cyber Evolution | LECS addresses this area with network-based detection that works alongside existing security tools.
Q2
How Does Cyber Evolution | LECS Approach Cyber Security Solutions in Europe?
Cyber Evolution | LECS uses its patented LECS platform for agentless Network Detection and Response. It examines network communications across IT, OT, and IoT environments using Deep Packet Inspection and behavioral analysis. The platform supports more than 300 communication protocols and can run as a physical appliance, virtual environment, cloud deployment, on-premises installation, or embedded and OEM solution. Because it does not require software on every device, organizations can extend network monitoring to equipment where agents are difficult or impractical to install.
Q3
What Features Matter When Evaluating Cyber Security Solutions in Europe?
Organizations evaluating Cyber Security Solutions in Europe should look at how much network activity a solution can see, which protocols it supports, how it handles alerts, and how easily it fits into existing security operations. An alert is more useful when it gives analysts enough context to understand what happened and decide what to do next. Integration with SOC and SIEM systems can also help teams work within processes they already use. Agentless monitoring can be particularly useful for legacy, industrial, medical, and embedded equipment that cannot easily support security software.
Q4
How Can Cyber Security Solutions in Europe Help Detect Lateral Movement?
Getting past the perimeter is only one stage of an attack. An attacker who reaches the internal network may then try to move between connected systems. Cyber Security Solutions in Europe can help identify that activity by examining east-west traffic and looking for behavior that differs from established patterns. LECS continuously analyzes network communications for anomalies and suspicious activity. In one documented deployment, it identified movement from a compromised Wi-Fi-connected host into an OT environment, isolated the affected system, and stopped the attack from progressing.
Q5
Why Does Alert Quality Matter in Cyber Security Solutions in Europe?
A high volume of alerts can make it harder for security teams to focus on genuine threats. Cyber Security Solutions in Europe should provide enough context to help analysts decide which events require attention. LECS uses behavioral analysis and network context to reduce unnecessary alerts. Company-reported field results show an average 87 percent reduction in false positives. Its integration with existing SOC and SIEM workflows also means security teams can work with the tools and processes they already have.
Q6
How Is Cyber Evolution | LECS Expanding Cyber Security Solutions in Europe?
Cyber Evolution | LECS is expanding through distributors, resellers, managed service providers, system integrators, and technology partners across 24 countries. Its platform can be deployed across different infrastructure models and used by organizations ranging from SMEs to large enterprises and critical environments. The company is also developing its network-focused approach around modular deployment, automated response, and compatibility with existing security stacks. This allows organizations to add network visibility without having to replace firewalls, EDR, SOC, or SIEM investments already in place.
Company
Cyber Evolution | LECS
Management
Mr. Roberto Camerinesi, Co-Founder and CTO
Description
Cyber Evolution | LECS is an Italian cybersecurity company and the developer of LECS, a patented, plug & play Network Detection and Response (NDR) technology for IT, OT, and IoT environments. Its agentless architecture, Deep Traffic Intelligence, real-time behavioral analysis, and autonomous response provide visibility into internal network traffic, detect lateral movement, reduce false positives, and complement existing security stacks without disrupting operations. Available through physical, virtual, embedded/OEM, cloud, and on-premise deployment models, LECS serves customers ranging from SMEs to large corporate organizations and integrates with SOC/SIEM environments through standard interfaces.
